 MentorX
 1
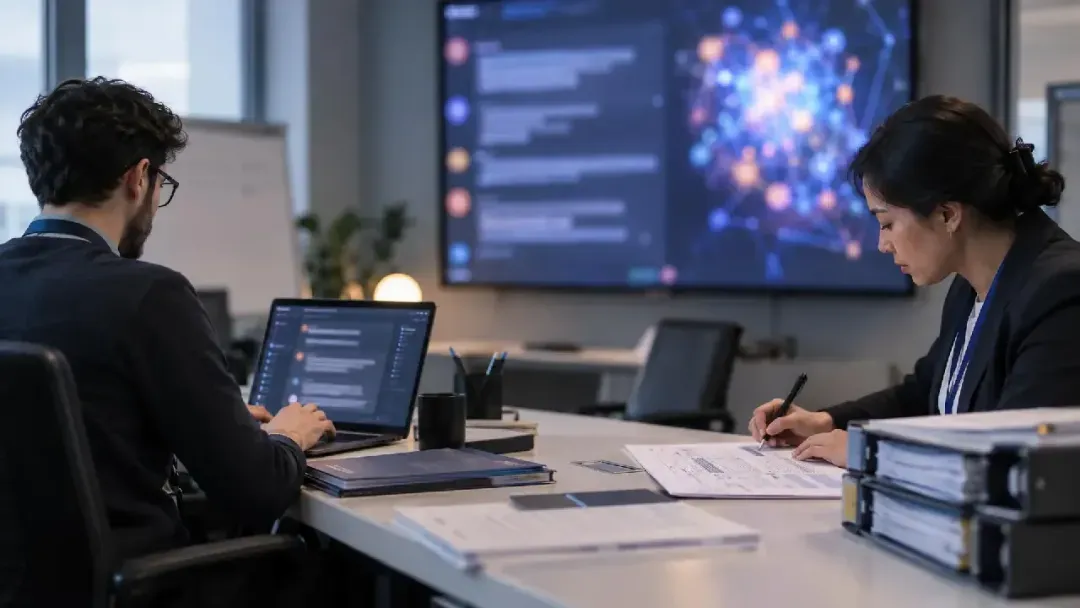
Going forward, accountants may not only audit financial books — they could also audit AI systems.
Over the past two years,
the line accounting students in North America hear most often
is probably that routine accounting work will sooner or later be replaced by AI.
But this time, AI may first deliver a new set of job opportunities for accountants in North America.
Automated bookkeeping, invoice recognition, financial statement generation and anomaly detection — many repetitive tasks are indeed being taken over by systems. Yet a recent move by the American Institute of CPAs (AICPA) reveals a different career angle: while AI cuts certain workloads, it also creates a new audit subject.
Going forward, accountants may not only audit financial books — they could also audit AI systems.
01 Companies Need Someone to Answer Whether Their AI Is Safe to Use
In October, the AICPA and the Artificial Intelligence Underwriting Company (AIUC) announced a joint assurance service, bundling the widely recognized SOC 2 report and the AIUC‑1 certification into a single CPA‑led engagement.
SOC 2 focuses on whether an organization’s information systems maintain robust controls for security, availability, confidentiality and privacy. AIUC‑1 goes one step further to verify whether AI systems and AI Agents are secure, stable and operating as intended.
Why is this kind of certification needed?
Today’s AI does far more than help employees draft emails or summarize meeting notes. Some AI Agents can call APIs, access client data, log into corporate accounts and even participate in approval and transaction workflows. If they leak sensitive data, fall victim to prompt injection attacks, or confidently produce incorrect outputs, the consequences extend beyond poor content quality — they can trigger genuine security incidents.
Companies can draft polished AI governance policies, but documentation on paper does not guarantee system reliability. This new joint assurance review examines not just processes and controls, but also runs practical tests on AI Agents for risks including hallucinations, data leakage, malicious requests and prompt injection.
It is somewhat like an annual health checkup for AI. It is not just about asking whether the system is running smoothly; it involves concrete metrics and stress testing to see whether it spirals out of control under edge cases.
02 This Is Not a Mandatory “AI Annual Inspection”, Yet the Trend Is Clear
It is important to note that this service is not a new government regulation, nor does it mean every company must obtain certification before deploying AI. It remains in early rollout. Some accounting firms have begun offering related services, with full launch expected in early 2027.
Still, the industry signal it sends deserves close attention. Once enterprises embed AI into finance, healthcare, financial services, customer support and internal operations, clients and investors will stop merely asking “Are you using AI?” They will follow up with tougher questions: “Is this AI secure?”, “Who is liable if something goes wrong?”, and “How do you prove it operates consistently?”
Historically, enterprises commonly required SOC 2 reports from software vendors during procurement. Going forward, AI safety and reliability certifications may gradually become part of procurement, risk management and compliance workflows for projects involving AI Agents.
This means AI governance is evolving from an internal policy document into a verifiable, testable professional service backed by formal reports.
03 Where Are the Opportunities for Accounting Job Seekers in North America?
What makes this new practice unique is that it sits neither purely within traditional audit nor fully within tech teams. It occupies an intersection of accounting, internal controls, data and cybersecurity.
Professionals needed for these future engagements must understand audit evidence, risk assessment and internal control frameworks. They also need to grasp how AI systems consume data, how permissions are configured, how model outputs are monitored, and who owns remediation when anomalies emerge.
Beyond traditional Audit and Tax tracks, accounting students in North America can start exploring IT Audit, Technology Risk, Risk Advisory, Cybersecurity Assurance, Data Governance and AI Governance. These roles already exist, but their scope will expand as AI penetrates core corporate workflows.
Students already pursuing CPA certification do not need to abruptly switch tracks to become algorithm engineers. A more realistic path is to build technical risk literacy on top of an accounting foundation — covering SOC 2, data privacy, access controls, model risk and AI governance. The scarce talent is not necessarily the best coder, but professionals who can translate risk between technical teams, leadership and audit clients.
AI will erode certain well-defined, repetitive finance tasks. Professionals limited to basic ticking-and-tying, template work and rigid procedural execution will face mounting pressure.
Yet the more AI companies deploy, the more systems, datasets and controls require validation. Accountants once audited financial statements, workflows and IT systems. Soon they may also verify whether AI oversteps access privileges, leaks data, and whether its judgments are explainable and traceable.
Books will still be audited. The next set of “books” to examine may belong to AI.